All case studies

Case study 02  Deep dive

Enterprise Tool Governance

Turning a fragmented enterprise-software administration process into a governed system—and exploring how AI could safely take on repetitive decisions within limits set by humans.

Real operational problem  Agentic AI concept

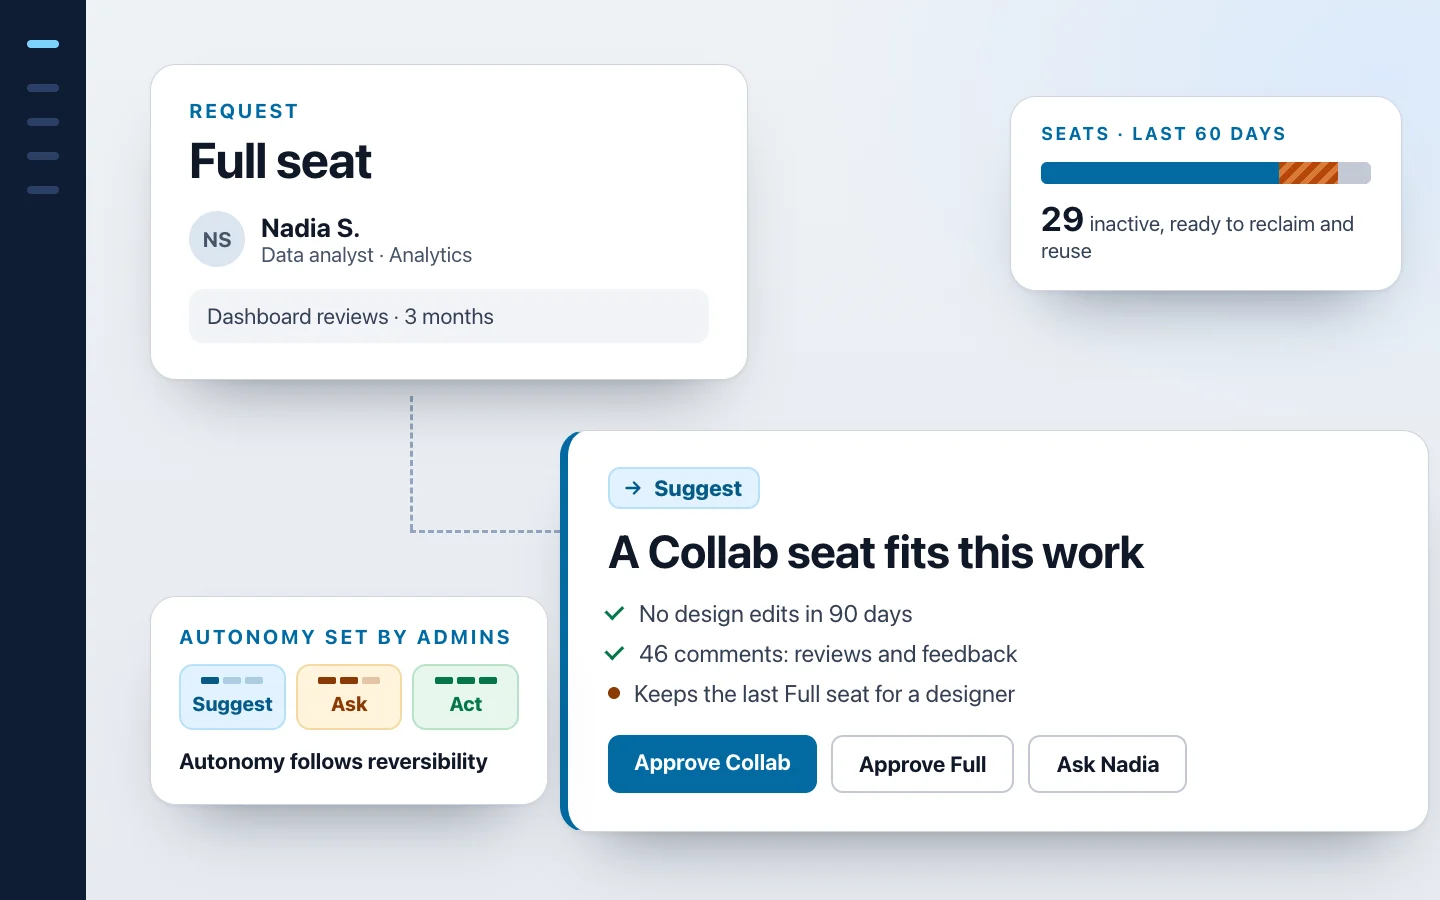
A request, an admin decision and a governance signal: a Full seat request for dashboard reviews, the agent suggesting a Collab seat with its reasons and an Approve Collab button, the Suggest, Ask, Act autonomy levels, and seat utilization with reclaim candidates
Role
Product / UX Design  Admin domain expert
Users
Employees, managers and enterprise-tool administrators
Domain
Enterprise software governance
Scope
Requests, allocation, utilization, cost visibility and AI-assisted governance
Status
Concept / working prototype based on a real operating problem

00  At a glance

The case in six lines

Product
An enterprise software-governance concept for Figma access, AI credits and plug-ins
Users
Employees, managers and enterprise-tool administrators
My contribution
Operational discovery, product strategy, UX/UI, the prototype and the Agentic AI interaction model
Evidence
Participant observation, admin communication analysis, a 285-request audit, admin agendas and a product and admin-console review
Status
A working concept and prototype based on a real operating problem
AI status
A rules-based prototype demonstrating bounded agent behavior

01  Operating problem

Ten admins. One enterprise account. No shared operating layer.

A global enterprise tool, Figma, was administered by a small, distributed group of admins whose primary jobs were elsewhere. I was one of them.

Requests and decisions were spread across
Chat messages
Email
Request forms
The vendor’s admin console
Admin coordination
User activity
AI-credit usage
Inactive-seat reviews
Plug-in and security requests
Organizational changes

Each request needed context that lived somewhere else: who the person was, what they would actually do, how many seats their team had left, whether they had asked before, and who would pay. Admins pieced that together one message at a time, in between their own work.

The enterprise admin console was only one part of the operating model. It held account and user information and the admin actions. The surrounding request, approval, communication and governance work remained fragmented.

Questions admins answered, one request at a time

  • Does this person actually need a paid seat?
  • Which seat type fits the work?
  • Is there an available seat to reuse?
  • Is an assigned seat inactive?
  • Should additional AI credits be approved?
  • Which admin should act?
  • Has the requester already asked?
  • What happens if usage changes later?

My role

I lived the problem before I designed for it

I was one of the admins managing the problem in addition to my primary design responsibilities. That gave me participant-observation access to the request patterns, admin coordination, recurring decisions and operational friction. I first explored the workflow as a conventional governance tool, then evolved it into an Agentic AI concept with explicit autonomy boundaries.

As an admin

  • Worked requests alongside the other admins
  • Took on the new-user request form, the first step toward structured intake
  • Took part in the monthly admin meetings on credits, plug-ins and inactive seats

As the designer

  • The operating model: lifecycle, roles and rules
  • The request, queue, policy, audit and insight experiences
  • The Agentic AI interaction model and its guardrails
  • A working prototype with test scenarios

The question it led to

How do you introduce AI autonomy into enterprise software governance without losing human control?

02  Evidence

What the evidence changed

No generic research phase: the evidence came from doing the work. Internal materials are summarized here, never shown, and names, workspaces and figures from them stay private.

  • Participant observation
  • Admin communication analysis
  • 285-request audit
  • Admin meeting agendas
  • Vendor console and documentation review
  • Participant observation: I was one of the admins doing the work.Changed: the design started from the decisions admins actually made, not from imagined personas. The roles are the real ones: requesters, their managers and admins.
  • Admin communication analysis: about a quarter of the admin group’s communication, reviewed for recurring patterns.Changed: requests arriving as direct messages, checks on how many seats were left, debates about inactivity cut-offs and requests for more AI credits became one structured intake, with availability visible at decision time.
  • Request audit: a request audit surfaced 285 open items across the admin group.Changed: a shared decision queue that any admin can work, sorted by what needs a person first.
  • Admin agendas: the same topics came back every month.Changed: new-user requests, inactive or unassigned users, AI-credit governance, plug-in governance and workspace changes made the lifecycle cover reclaim, reuse, credits and plug-ins, not just new seats.
  • Rules the admins already agreed: plug-ins had criteria (built by vendor partners, security information available, no third-party payments), and AI credits had a monthly allowance per approved request.Changed: these became checkable policies. Plug-in requests stay at Suggest; top-ups within the allowance are a candidate for Act.
  • Vendor console and documentation review.Changed: the console holds account, user and usage information and admin actions, so the concept is designed as an operating layer around it. It doesn’t assume integrations that weren’t verified.

03  Governance model

The problem was not assigning seats. It was governing decisions over time.

A simple request form would not solve the things the admins kept returning to. Each needs a decision now and a check later.

What a form alone doesn’t handle
Repeated requests
Inactive users
Budget pressure
Exceptions
Temporary needs
AI-credit usage
Reallocations
Offboarding
Unclear ownership
  1. Request

    Someone asks for access, a different seat type or more AI credits.

  2. Evaluate

    Need, role, budget, availability and policy.

  3. Assign

    Provision the access that fits the work, not the most expensive one.

  4. Monitor

    Watch activity, credit use and limits over time.

  5. Reclaim

    Recover underused access, with the owner told first.

  6. Reuse

    Allocate existing capacity before buying more. Reuse feeds the next request.

The real product was the operating model around the license.

04  Product strategy

I redesigned the operating model before designing the AI.

If rules, roles and escape routes are unclear, an AI agent only automates inconsistency. So the governance structure came first, and each layer had to exist before the next one could be trusted.

  1. FoundationFirstCentralize requests and governance in one place.
  2. VisibilityThenExpose status, usage, allocation and exceptions.
  3. RulesThenDefine policies, thresholds and admin controls.
  4. AutomationThenAutomate repetitive, low-risk actions.
  5. Agentic layerLastAllow bounded autonomous behavior only after the controls exist.

Evolution

From a conventional tool to a bounded agentic system

Stage 1

Make the process visible

The original concept, built in Figma Make, focused on the workflow itself:

  • Request intake
  • Seat assignment
  • Cost tracking
  • Request status
  • Admin management
  • Insights and reporting

Stage 2

Add bounded AI

Once the workflow was structured, I explored where AI could reduce repetitive admin work:

  • Read the signals an admin would check
  • Recommend, ask or act, by policy
  • Gather missing context from requesters
  • Undo, audit and escalation on every action
  • A bypass to a human, always

The requirements document, used honestly

A requirements document was written from the evolving concept. It models seat inventory, assignment, reassignment and reclaim, cost tracking, request workflows, reporting, roles, an audit trail, admin controls and integrations.

Most of its scope is explicitly marked as assumptions to confirm, so it is shown here as requirements modeling, not as researched or validated scope.

05  Agentic AI

Suggest → Ask → Act

The agent reads the signals an admin would check, then does one of three things. Which one is not the model’s choice: it follows policy set by admins for each kind of request.

  1. Lowest autonomy

    Suggest

    The system recommends an action but does not execute it.

    Typical triggers

    • An inactive seat
    • An unusual request
    • An ambiguous project need
    • Sparse context
    • A high-cost or sensitive exception
  2. Pauses for a person

    Ask

    The system stops and asks an admin, or the requester, for a decision.

    Typical triggers

    • Missing information
    • Conflicting signals
    • Exceptions
    • Policy uncertainty
  3. Highest autonomy, still bounded

    Act

    The system executes reversible, low-risk actions within rules admins define.

    Concept examples

    • A Dev or Collab seat that fits the role, while the team has seats
    • An AI-credit top-up within the monthly allowance
    • Every action undoable for 24 hours

Autonomy principleAutonomy follows reversibility.

The harder an action is to reverse, or the more financial or security impact it carries, the less the agent may do on its own. That one rule decides which requests land in Suggest, Ask or Act.

The prototype uses rule-based logic as a stand-in for an AI agent. There is no production model integration: the goal is to test the interaction patterns, the autonomy boundaries and admin trust.

06  Experience

Key design moments

Serious enterprise admin software: dense, structured and governed. Each screen is recreated with sample data, white-label and without employer branding, with the problem it addressed, the decision and why. Names, numbers and policies are examples.

A

A self-service request entry

Problem
Requests arrived through chats, email and forms, each with different, often missing, information.
Decision
One entry point with a request type, plain-language choices for what the person will do, and the status of every request in one place.
Why
Governance starts with consistent, structured information. A request that already says what the work is can be decided, or automated, safely.
Recreated screen · sample data. Employee request screen: a request type switch for seat, AI credits or plug-in, four plain-language choices for what the person will do in Figma, with the Dev seat marked as fitting their role, fields for project, duration and purpose, the manager added automatically, and a link to talk to an admin instead
B

The admin decision queue

Problem
Admins had no shared, prioritized view: each one worked from their own messages.
Decision
A queue showing request context, status, risk and usage signals, and the recommended next step, with what needs a person first.
Why
It turns coordination between admins into a visible operating system, and any admin can pick up any request.
Recreated screen · sample data. Admin decision queue: five requests with the requester, the request, a signal such as team at its limit, reviews only, little context, inactive or fits role, and the next step shown as Ask, Suggest or Act. The selected request opens a side panel: a Full seat request with no design edits and 46 comments in 90 days, one Full seat left in the team, a suggestion to approve a Collab seat with the reasons, and buttons to approve Collab, approve Full or ask the requester
C

Suggest → Ask → Act, set by policy

Problem
Not every request should get the same level of automation.
Decision
Make autonomy explicit and policy-controlled: admins decide which kinds of request the agent may act on, only suggest, or must ask about.
Why
Admins can always tell whether the system is recommending, requesting approval or acting.
Recreated screen · sample data · policies are examples. Agent policy screen set by admins: six kinds of request mapped to what the agent may do. It may Act on a Dev or Collab seat that fits the role and on an AI-credit top-up within the monthly allowance, both with a 24-hour undo. It may only Suggest for a Full seat, a seat inactive 60 days or more, or a plug-in request. It must Ask when context is missing, signals conflict or the team is at its limit. Below, safety controls: 24-hour undo on, a circuit breaker that drops the agent back to Suggest after three undos, and a Pause agent button
D

Undo, audit and reasoning

Problem
Enterprise admins need accountability and a way to recover from a wrong call.
Decision
Make every action reversible and inspectable: a 24-hour undo, a reason on every entry, and admin overrides logged next to the agent’s actions.
Why
Trust comes from control, not from pretending the AI is always correct.
Recreated screen · sample data. Audit log: a confirmation that the agent approved a Dev seat with undo available for 23 hours, then a timeline of five actions with time, mode and reason: an approved Dev seat with its rule and an Undo button, a suggestion of Collab instead of Full waiting for an admin, an admin overriding the agent with the reason given, the agent asking a requester two questions, and an AI-credit top-up within the allowance
E

Insights: utilization in one view

Problem
Inactive seats and credit use were reviewed by hand, in meetings and spreadsheets, when renewal came round.
Decision
Connect seat and activity data to admin decisions: active, inactive and unassigned seats by team, AI-credit use, and a direct path to the reclaim review.
Why
Reclaim and reuse become a routine step in the lifecycle instead of a yearly clean-up. No savings are claimed from sample data.
Recreated screen · sample data. Insights: four tiles for seats assigned, active seats, seats inactive 60 days or more as reclaim candidates, and the share of the AI-credit pool used. A bar per team splits seats into active, inactive and unassigned, with a legend that uses a pattern for inactive. Buttons to review the reclaim candidates and export for renewal planning
F

Ask, with a human bypass

Problem
Sparse requests such as “Need Figma for a project” forced admins to chase people for context.
Decision
The agent asks the requester two specific questions and holds the request. A visible link skips the agent and goes to an admin, keeping the request’s place.
Why
The agent gathers what an admin would ask for, but never stands between a person and a human decision.
Recreated screen · sample data. Requester view of a request on hold: a tracker at the agent review step, and a card where the agent asks two questions because the request only said need Figma for a project: what the person will do in Figma, and which project and until when. Buttons to send the answers or skip the agent and talk to an admin, with a note that skipping keeps their place

Working prototype

Test the governance agent

This working prototype combines the original governance workflow with a simulated Agentic AI layer. The agent behavior is rules-based for demonstration; the goal is to test interaction patterns, autonomy boundaries and admin trust—not claim a production AI implementation. Pick a scenario to run it.

Earlier working prototype. The interaction model was built first to test the governance flow and agent behaviors; the case-study screens above show the evolved visual and product direction.

Enterprise Tool Governance  prototypeOpen full screen ↗ (opens in a new tab)

The prototype is a desktop-sized app, so it opens best in its own tab.

Test the governance agent (opens in a new tab)

07  Guardrails

Eleven guardrails, so admins stay in control

The concept treats safety as product design, not as a settings page added at the end.

  • Admin-set autonomy limits

    Admins decide, per kind of request, whether the agent may act, only suggest, or must ask.

  • 24-hour undo

    Every agent action can be reversed for a day, by an admin or by the rule that took it.

  • Circuit breaker

    Too many undos in a day drops the agent back to Suggest until an admin reviews it.

  • Pause and kill switch

    Any admin can pause the agent at once; requests keep flowing to people.

  • Human bypass

    Requesters can skip the agent and go to an admin, keeping their place.

  • Visible reasoning

    Each decision shows the signals it used and why, in words.

  • Audit trail

    Every action records who or what took it, the rule, the reason and the time.

  • Escalation

    Exceptions, conflicts and teams at their limit always reach a person.

  • Role-based permissions

    Requesters, managers and admins each see and do only what their role allows.

  • No policy editing by the model

    Policies live in a layer the agent can read but never change.

  • Fallback to Suggest

    When confidence is low or rules conflict, the agent recommends instead of acting.

The prototype uses rule-based logic as a stand-in for an AI agent. There is no production model integration: the goal is to test the interaction patterns, the autonomy boundaries and admin trust.

08  Outcome

What the evidence shows, and what is modeled

Strict labels: observed, operational, modeled and status are kept apart, and no savings are claimed from sample data.

  • Observed evidence

    Recurring admin coordination was fragmented across channels. Multiple governance topics appeared repeatedly in admin agendas, and the request audit showed 285 open items across the admin group.

  • Operational outcome

    The concept centralizes the request, allocation and governance workflow, with one lifecycle, explicit roles and rules, and escape routes for everyone.

  • Modeled outcome

    About 80 → 15 admin hours a month in the concept’s model, from illustrative assumptions about request volume, time per decision and the share the agent could resolve within policy.

    Modeled scenario — not production data

  • Project status

    A concept and working prototype based on a real operating problem. The autonomous governance system was not deployed, and the agent in the prototype is rules-based.

Future product direction

Requester-first access, governed administration

In a production implementation, employees would start in a company-hosted requester portal to request Figma seats or AI credits and track decisions. A separate, role-restricted administrative workspace would support queue review, license allocation, policy controls and audit history.

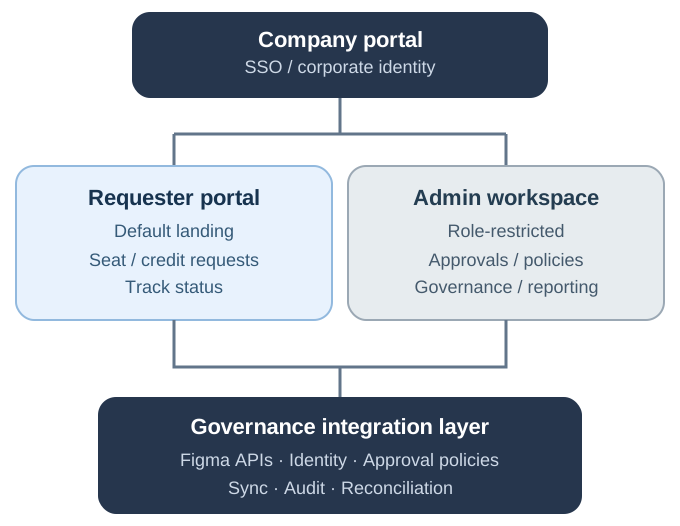
Proposed architecture: corporate SSO leads to the default requester portal and a role-restricted admin workspace, supported by a shared Figma integration and governance layer.
Conceptual future-state architecture. Enterprise SSO, Figma API integration, provisioning, synchronization and reconciliation are not implemented in this rules-based prototype.

This layer would complement Figma's native administration, not replace it. Actual seat provisioning, usage signals and API coverage would require enterprise integration validation before implementation.

Reflection

Reflection

The most important design decision was not how much the AI could do. It was deciding what the AI should never do without a human-controlled operating model around it.

The project reinforced that enterprise AI trust comes from explicit rules, reversibility, visibility and escalation—not from maximizing autonomy.

Want to talk through the work?

I’m happy to walk through this project, the decisions behind it and what I’d do next, in more detail.